FBI Shutdown Prolific Ransomware Group “Radar/Dispossessor,” Domains Seized
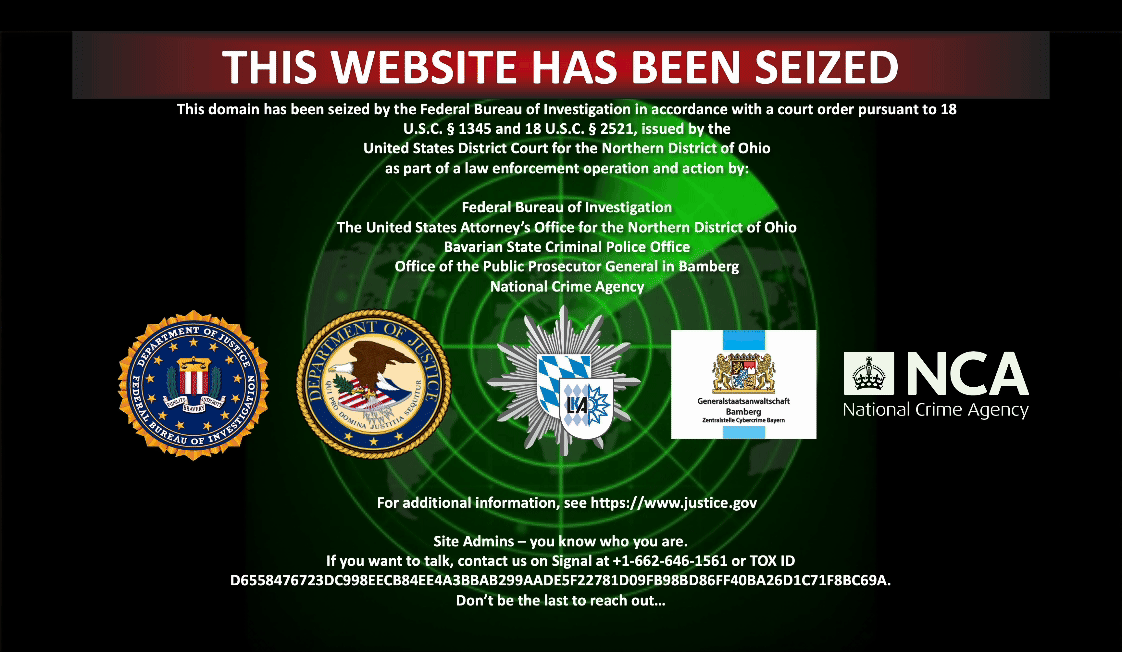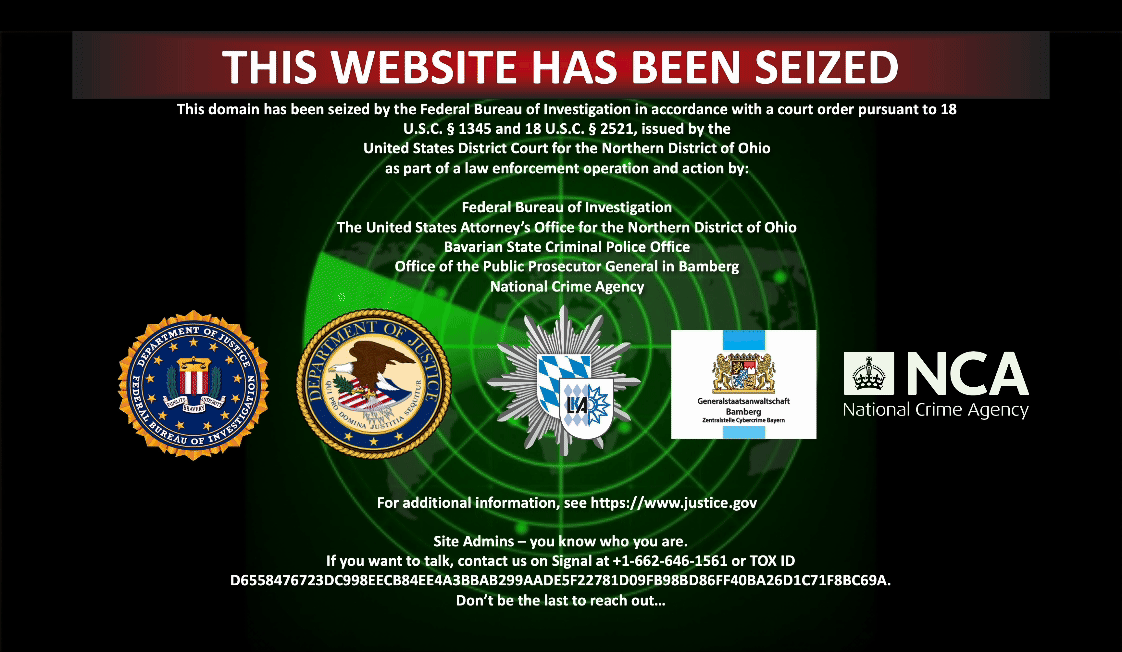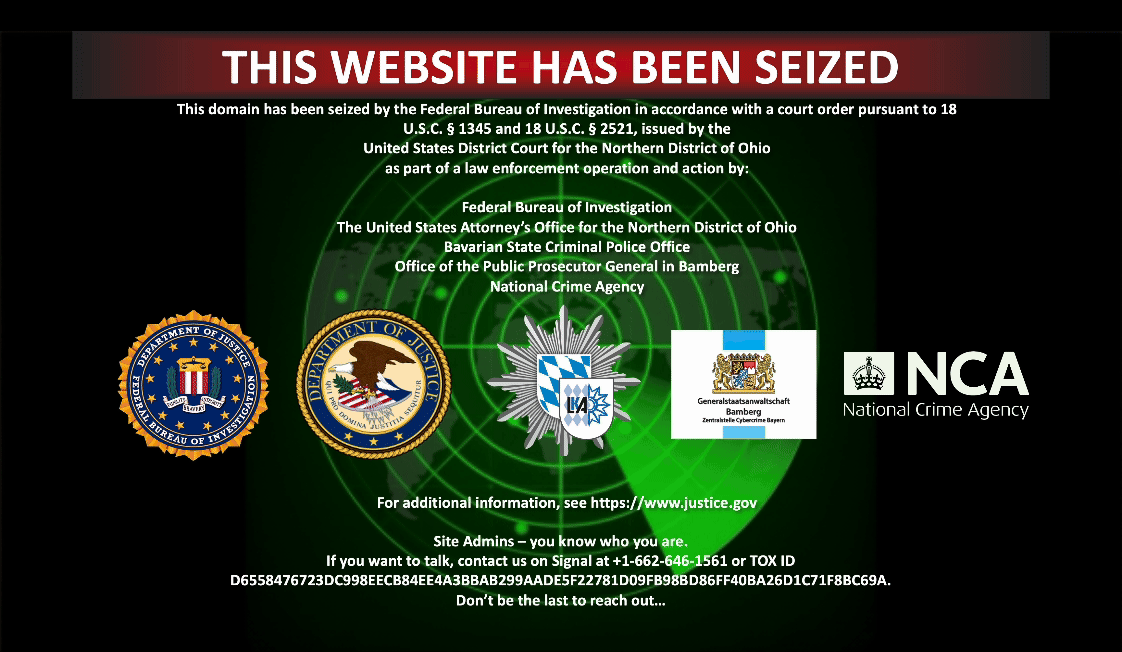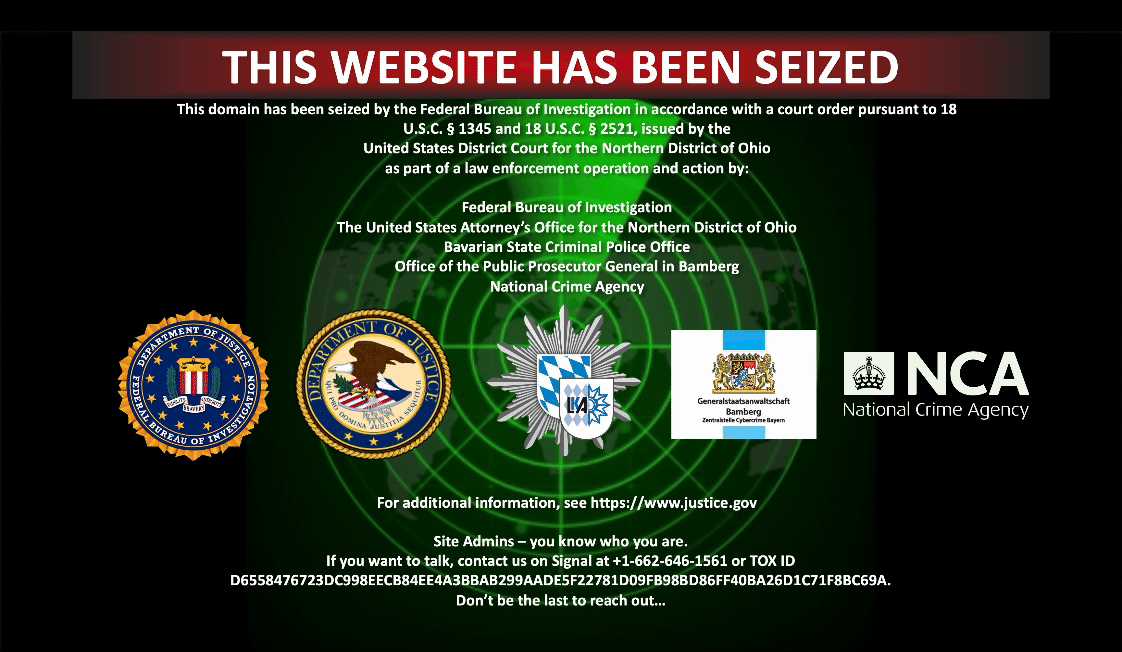
WASHINGTON, D.C. – The FBI has announced they have shut down a prolific ransomware group known as “Radar/Dispossessor” and seized multiple internet domains and servers utilized by the cyber threat actors, reportedly headed up by an individual known by the code-name “Brain.”
As part of the FBI’s enforcement actions, they have dismantled a plethora of servers utilized by Radar/Dispossessor to carry out their ransomware attacks, including three in the United States, three in the United Kingdom, and 18 in Germany. In addition, the seized criminal domains include eight based in the U.S. and one German domain.
Radar/Dispossessor first came on the FBI’s radar in August 2023, and as their profile continued to raise in the internet’s underworld, law enforcement began devoting more and more resources to identify and, ultimately, take them down.
The group was known for concentrating their illicit efforts on small-to mid-sized businesses and organizations in the production, development, education, healthcare, financial services, and transportation fields. U.S-based entities were the initial targets, but the scope of Radar/Dispossessor’s victims grew over time to include other countries as well, with eventually 43 companies – located in Argentina, Australia, Belgium, Brazil, Honduras, India, Canada, Croatia, Peru, Poland, the United Kingdom, the United Arab Emirates, and Germany – falling prey to their attacks.
Radar/Dispossessor would utilize ransomware to extort the companies in question by stealing their critical data. They did this by tracking down and identifying weaknesses in a potential victim’s digital network, such as vulnerabilities in their computer systems, weak security passwords, or a lack of two-factor authentication protocol for access.
Once the critical data had been exfiltrated to the attacker’s server and solidly encrypted in the victim’s system, Radar/Dispossessor would then force the company to pay to get it back; failure to meet the group’s demands would result in the data either being publicly leaked and/or destroyed. However, the FBI notes that paying the ransom does not guarantee the attacked files will eventually be decrypted.
The FBI requests that any victims of Radar/Dispossessor – or those with information on the group’s dealings, including its leader, Brain – to contact its Internet Crime Complaint Center at ic3.gov or 1-800-CALL-FBI.
John Colascione is Chief Executive Officer of SEARCHEN NETWORKS®, a digital marketing and technology company founded in 2001. An entrepreneur, author, and digital publisher with more than 25 years of experience, he specializes in search engine marketing, Website Monetization, domain names, and online business development. He is the author of Mastering Your Website and publishes commentary on technology, digital marketing, and the evolving Internet economy. Read more at JohnColascione.com.
Add STRATEGIC REVENUE as a Google Preferred Source to see more of our business, technology, and digital strategy coverage in Google Search.
Add Strategic RevenueYou can now select the categories you're interested in and receive email updates when new articles are published in only those categories.