Vulnerability In Official Facebook Chat Plugin Allowed Attackers to Chat With Site Visitors
WEST PALM BEACH, FL – At 3:47 PM today, the Threat Intelligence Team from WordFence, posted research detailing a vulnerability in The Official Facebook Chat Plugin, currently installed on over 80,000 WordPress websites. This vulnerability allowed authenticated attackers to connect their own Facebook Messenger account to any site running the vulnerable plugin and engage in chats with site visitors on affected sites.
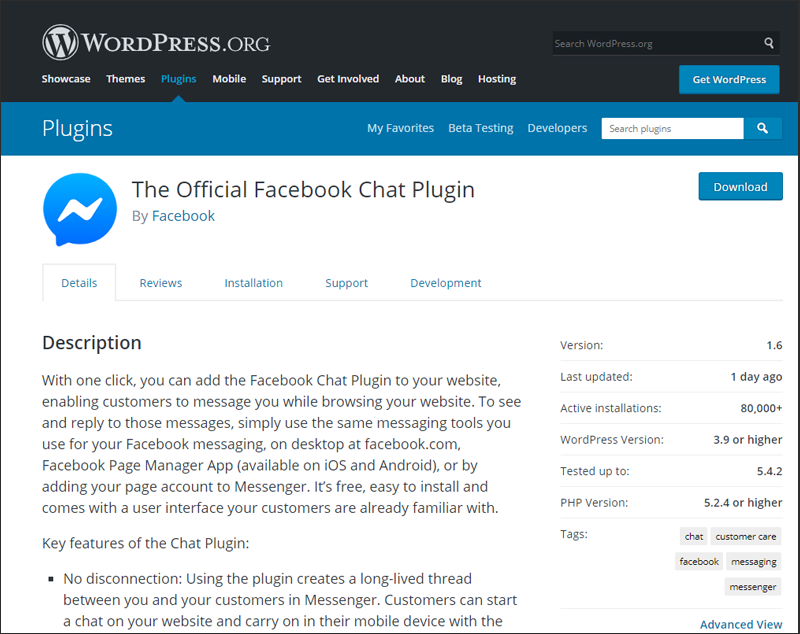
We initially reached out to Facebook on June 26, 2020 and included the full disclosure details at the time of reaching out. They initially responded on June 30, 2020, and after much back and forth, Facebook released a patch on July 28, 2020. We highly recommend updating to version 1.6 immediately to keep your site protected against any attacks attempting to exploit this vulnerability.
The Wordfence WordPress security plugin provides free enterprise-class WordPress security, protecting your website from hacks and malware. Real-time IP Blacklisting, Firewall Rule Updates and Real-time Malware Signature Updates are available for premium paid users.
John Colascione is Chief Executive Officer of SEARCHEN NETWORKS®, a digital marketing and technology company founded in 2001. An entrepreneur, author, and digital publisher with more than 25 years of experience, he specializes in search engine marketing, Website Monetization, domain names, and online business development. He is the author of Mastering Your Website and publishes commentary on technology, digital marketing, and the evolving Internet economy. Read more at JohnColascione.com.
Add STRATEGIC REVENUE as a Google Preferred Source to see more of our business, technology, and digital strategy coverage in Google Search.
Add Strategic RevenueYou can now select the categories you're interested in and receive email updates when new articles are published in only those categories.